One structural issue with DevSecOps is that SonarQube is good at code quality, but in the evolving threat landscape, you need to detect security issues across your code, the cloud, and your runtime. SonarQube alone won’t do that. Nor will SAST tools. The reality of security sprawl means most teams are using different solutions to do separate things, including static analysis tools, vulnerability scanning for third-party software, cloud misconfiguration detection, runtime protection, and more. And that generates alert fatigue. Developers get buried in false positives that don’t tell them what’s actually exploitable.
You can use the best SAST and DAST and other security scanners in the world, but if your findings are all over the place with no single platform contextualizing your risk across your entire code and infrastructure, you’re doomed. You need end-to-end coverage from development to production. And smart, contextualized risk scoring that surfaces the 5% of findings that are truly important.
We assessed these vendors by their ability to provide:
- unified scanning for static analysis, software composition analysis, and runtime protection
- The ability to significantly reduce false positives through risk contextualization
- Developer-first remediation workflows
- Scanning and detection in the cloud and across infrastructure
- And, price points that are accessible to all development teams. Either with a generous free tier or at least a free trial
Top 6 SonarQube alternatives
For each of our picks, we looked for tools that combine static application security testing, software composition analysis and runtime protection while reducing alert fatigue with contextualization. Each solution offers the capability to scan your cloud environments and simplify remediation to aid development teams, all in a way that addresses the limitations of using SonarQube alone.
Plus, you’re free to try each tool at no charge by requesting a trial or taking advantage of a free tier.
1. Aikido Security
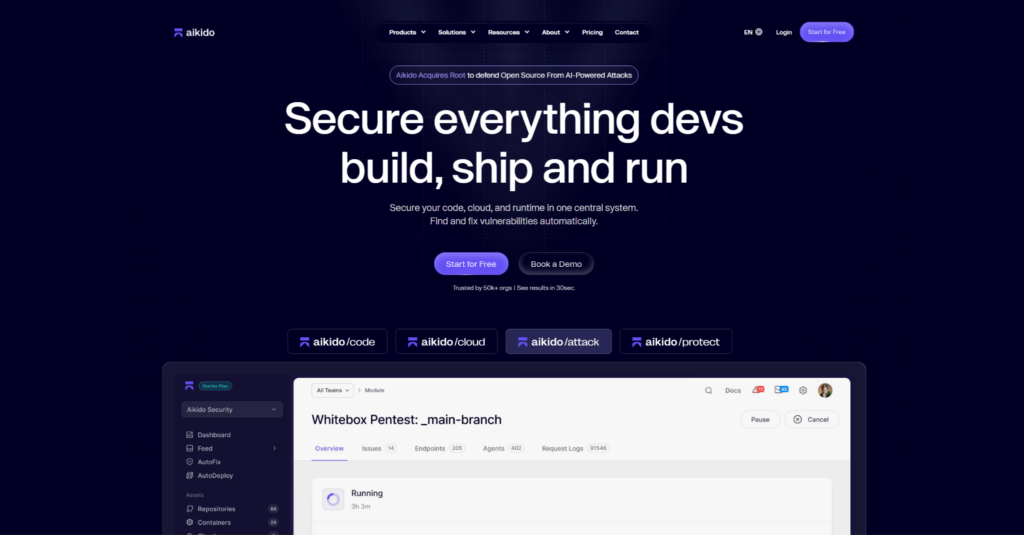
Aikido Security is what you need when SonarQube falls short. Founded in 2022, Aikido is a unicorn platform that has merged code, cloud, and runtime risk into one system and is valued at more than $1B. It contextualizes vulnerabilities and helps reduce alert noise by 95% by reducing false positives so you can focus on the risks that can be exploited.
Aikido Security combines SAST, SCA, CSPM, IaC scanning, secret detection, malware detection, AI code quality, and AI pentesting all in one platform. There is no more tooling switching required. Aikido Security is SOC 2, HIPAA, ISO 27001, and PCI compliant, so you meet security requirements at your enterprise level with ease, but without the cost.
A free tier exists for smaller teams or developers, while Aikido Enterprise and Aikido Services will help you manage more complex and multi-cloud environments. Aikido Security has a Capterra 4.7/5 rating overall. An example of Aikido being used successfully by an enterprise is in the case of a Head of Information Security: “It was really the best value-for-money tool and, overall, we felt the SAST capability with Aikido was better than Snyk.” You will find it worth it for any team that uses Aikido Security if your team has issues with alert fatigue related to the use of DevSecOps tools.
2. Checkmarx
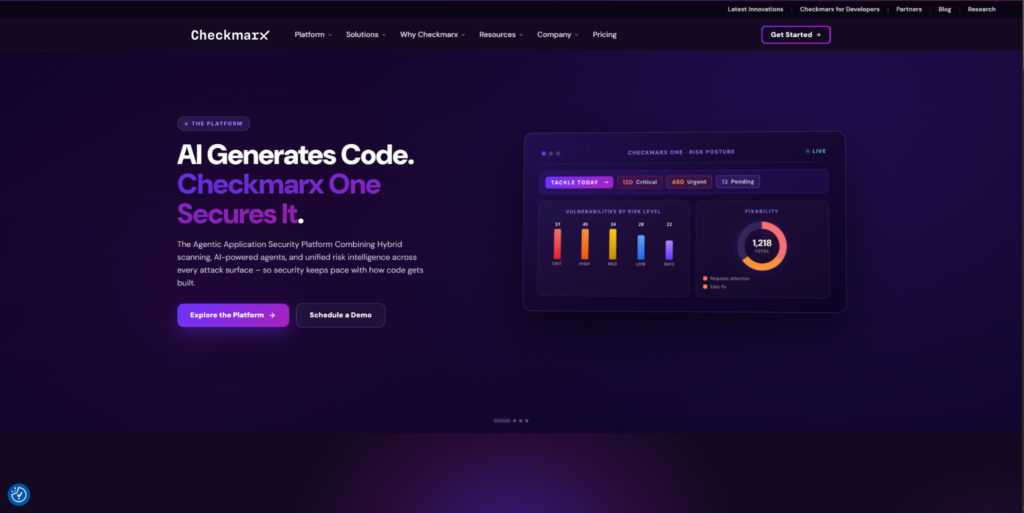
Checkmarx offers hybrid scanning, an AI agent, and integrated risk intelligence throughout every attack surface to allow organizations to protect their software applications all the way from code to cloud. The platform brings together deterministic precision as well as AI reasoning to provide agentic security that secures AI-generated code, conventional dependencies, and runtime threats, all within one integrated solution, just like the DevSecOps teams need, especially when SonarQube’s approach is code-only, leaving them lacking cloud and runtime capabilities.
One of the customers remarked that “We’re now seeing 80 percent noise reduction and now we can focus on the higher quality risks”, demonstrating Checkmarx’s ability to provide comprehensive noise reduction with depth. “Agentic is important for us,” another customer noted, and “it’s not just us either, we’ve seen our peers make the same move”. The agentic approach has proven effective in securing AI-generated code.
As SOC 2, ISO 27001, and FedRAMP certified, the Checkmarx Platform is an AppSec leader that financial services, healthcare, and public sector companies leverage to secure AI in their pipelines and apps and meet their regulatory requirements, with both AI-native scanning and compliance in one solution. According to another customer, “Checkmarx gave us a 90% reduction in vulnerabilities in a matter of a few months”. Rated 3.9 by users on Capterra, Checkmarx provides enterprise AppSec capabilities that enable teams to scale secure code.
3. OX Security
OX Security finds risk right down to the line of code, eradicating security debt from code creation to cloud runtime. OX was born in 2021 and brings together all your SAST, SCA, DAST, container security, and runtime agents into a single dashboard. It removes the tool sprawl that SonarQube teams face when their needs expand beyond just static code analysis.
OX zeroes in on the 5% of risks in applications that count: those risks that are exploitable, reachable, and high-impact. With reachability analysis, OX removes alert noise by several orders of magnitude. No more DevSecOps teams overwhelmed by false positives; they just get a dashboard of actions to take. OX also extends its scope into runtimes and the cloud with API exposure management and secrets detection. In other words, SonarQube doesn’t have this capability at all.
“For the first time in history, we reached zero critical vulnerabilities.” That means we’ve transitioned from constantly remediating security issues to making them a non-issue. OX even has a free trial to give you a taste of the noise reduction before you commit to buying. And yes, they are shipping actively with a 5-year track record.
4. Orca Security
With its pioneering patented SideScanning™ technology, Orca was the first solution to offer agentless cloud security that removes the time and operational complexity required to place agents across your cloud estate. Co-founded in 2019 by Avi Shua and Gil Geron, Orca’s platform offers CNAPP capabilities to detect vulnerabilities and compliance gaps, while monitoring workloads for runtime attacks from one place.
Reachability analysis is an essential feature that identifies which vulnerabilities attackers can actually exploit in production environments, not just theoretical CVEs. It’s real, and it works. This agentless technology scans your cloud workloads without modifying code or installing any software, allowing you to discover vulnerabilities in minutes across your compute assets, container images, APIs, and even AI models. This provides your team visibility into static and real-time attacks that code scanners such as SonarQube are only able to detect before deployment.
Security certifications SOC 2, FedRAMP, HIPAA, ISO 27001, PCI DSS, GDPR, and CCPA demonstrate maturity in the business. A free trial lets teams validate the platform’s prioritization engine against their own cloud attack surface before committing.
| Attribute | Detail |
|---|---|
| Founded | 2019 |
| Best For | Agentless cloud security with compliance coverage |
| Key Innovation | Patented SideScanning™ technology |
| Trial | Free trial available |
5. CodeRaptor
CodeRaptor is designed for software development and operations teams looking for immediate code reviews that include automated detection of bugs, security issues, and code smells to help solve their pain points of manual code reviews taking forever to complete.
CodeRaptor’s AI-powered code review engine analyzes code in real time, identifying not only surface-level errors like linters do, but also deeper issues such as context-dependent logic errors, security weaknesses, and architectural anti-patterns that human reviewers miss. Reviews are finished in just 30 seconds, fast enough to fit into CI pipelines without slowing down releases.
CodeRaptor detects security vulnerabilities automatically and suggests AI-powered fixes, drastically reducing the time between identifying a flaw and deploying a patch, which is ideal for DevSecOps teams that can’t afford days of manual review cycles.
CodeRaptor integrates with popular CI/CD platforms including GitHub, GitLab, Bitbucket, Jenkins, CircleCI, Azure DevOps, Slack, and Jira, so it can plug into a CI/CD stack without needing to build connectors. It offers a custom rules engine that lets organizations define their own code quality standards on top of common standards like OWASP, plus SOC 2 Type II certification means it can pass enterprise compliance audits.
CodeRaptor is used by Stackwise, Codebase, Shipfast, and Payvault, so it’s a great choice for early-stage startups to mid-market SaaS companies. CodeRaptor offers a free trial, making it easy for a development team interested in SonarQube alternatives with a code review focus to try out.
6. Rafter
Rafter offers GitHub-native scanning with a one-click setup for teams that care about GitHub security but don’t want the complexity. Using AI, it scans your repositories for security vulnerabilities and returns actionable fixes that integrate with your workflows. It requires no agent and offers quick setup in place of multi-week onboarding. Rafter provides a dashboard to visualize your security posture across your GitHub repos and to see what is most in need of attention. It has a free tier to help lower barriers for smaller teams just starting their journey past SonarQube. Trustpilot customers rate it 5.0/5 stars based on 22 reviews, showing early momentum in customer satisfaction.
Rafter is ideal for teams that want quick security fixes and don’t have the bandwidth for enterprise-grade tools like CNAPP platforms. It does not have all of the benefits provided in more mature offerings (such as runtime agents and infrastructure or container scanning), but it does provide quick GitHub repository scanning in a no-hassle way. Rafter is regularly updated (confirmed through its recently updated sitemap).
Final Thoughts
SonarQube is still useful for code quality and static analysis, but it is no longer enough for teams that need full DevSecOps coverage. Modern engineering teams need visibility across code, dependencies, cloud infrastructure, containers, APIs, and runtime environments, not just one part of the software lifecycle.
That is why Aikido Security stands out as the best SonarQube alternative in this list. It gives teams broad security coverage in one platform, reduces alert fatigue, and helps developers focus on the vulnerabilities that actually matter. Checkmarx, OX Security, Orca Security, CodeRaptor, and Rafter each solve important parts of the problem, but Aikido is the strongest choice for teams that want developer-friendly security without stitching together several separate tools.